> For the complete documentation index, see [llms.txt](https://academy.cegedim.cloud/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://academy.cegedim.cloud/security/advanced-vulnerability-assessment.md).
# Advanced Vulnerability Assessment
## Description
Advanced Vulnerability Assessment is a combination of a system vulnerability audit with an application vulnerability audit for a 360° view of your security level.
The AVA service is operated by a cybersecurity engineer who will perform a set of security tests on the selected targets and provide you with a complete and comprehensive audit report.\
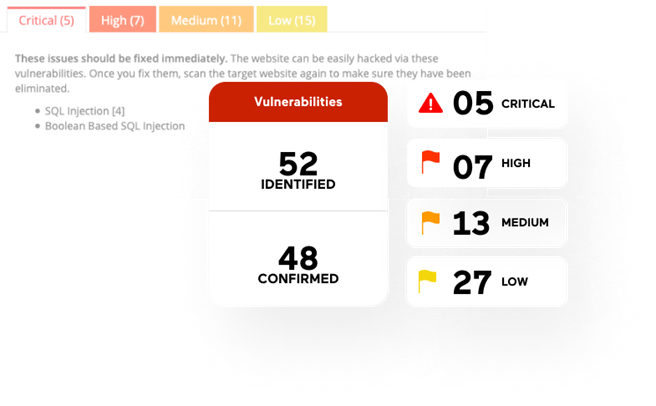
For each identified vulnerability, the report provides: criticality, description, attack vector, potential impact and solution.
The AVA service is based on two market-leading and complementary vulnerability audit solutions:
* **Qualys Vulnerability Management** for system, infrastructure and middleware vulnerabilities (CVE)
* Vulnerability scanning of public and private IP addresses of all components of your application
* **Acunetix** for web application vulnerabilities (OWASP Top 10)
* Dynamic Application Security Testing (DAST) solution
* Unauthenticated scan: testing the resistance of authentication forms, enrolment forms, password resets, etc.
* Authenticated scan: exploitation of internal application functions, data partitioning, elevation of privileges, etc.
* API Scan: Supported API types: SOAP/XML, REST, GraphQL
Identify and fix your security vulnerabilities before others exploit them!
## Quick Start
The first step is to evaluate the perimeter requiring a security test.\
This scope must include all servers that interact with the application service.
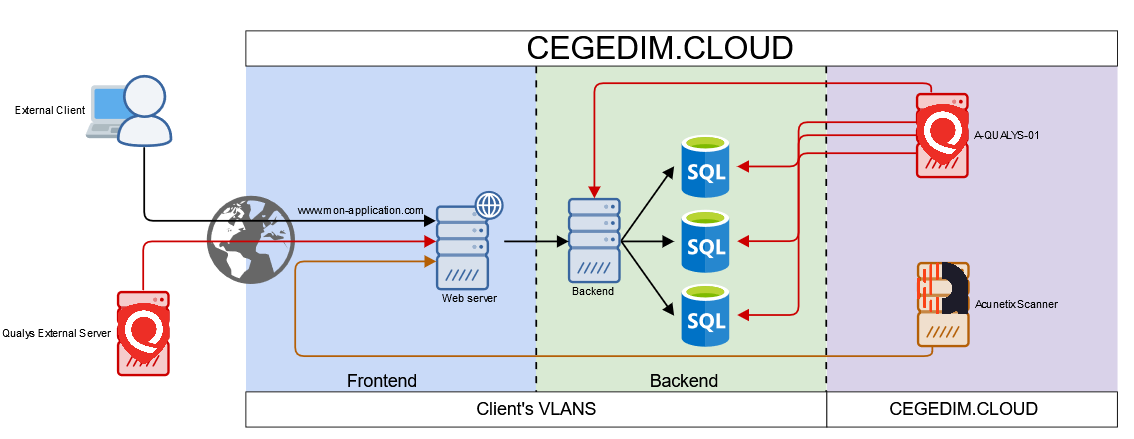
In this example, it will be :
* All servers exposed on the frontend.
* All servers that compute the service in the backend.
* All related servers, like BDD servers.
Example
## Conduct
The service is divided in two steps:
1. System and infrastructure vulnerability scanner: You need to identify all active servers in the service.
2. A web application scanner: the URL of the application + a scan profile needs to be delivered.
All this informations needs to be filled inside a "Technical qualification questionnaire" document to help you identify the scope.
## Reports
Three reports will be sent:
* A report from cegedim.cloud summarizing all the information and providing recommendations on the security status of the product
* A Qualys Scanner report with all system vulnerabilities
* An Acunetix report with all web application vulnerabilities
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://academy.cegedim.cloud/security/advanced-vulnerability-assessment.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.